One login for every application.
Extended, integrated, operated.
Single sign-on with Keycloak: we extend it where the standard ends, connect it to your applications and existing accounts and run it highly available on Exoscale — from two-factor authentication to login with ID Austria.
- Open source, no per-user cost
- SSO with OIDC & SAML
- ID Austria · Entra ID · ADFS
- Operated on Exoscale
Typical starting points
Keycloak is the open-source standard for login, single sign-on and permissions. These are the situations customers come to us with:
- Several applications, several logins — with single sign-on, users sign in only once
- A customer portal needs sign-up, password reset and two-factor login
- A SaaS application needs separate tenants with their own users and roles
- Employees should sign in with their company account — via Entra ID or the on-premises Active Directory via ADFS
- A service needs a reliable identity — login with ID Austria
- Two-factor authentication is required, for example by customers or as a measure under NIS2
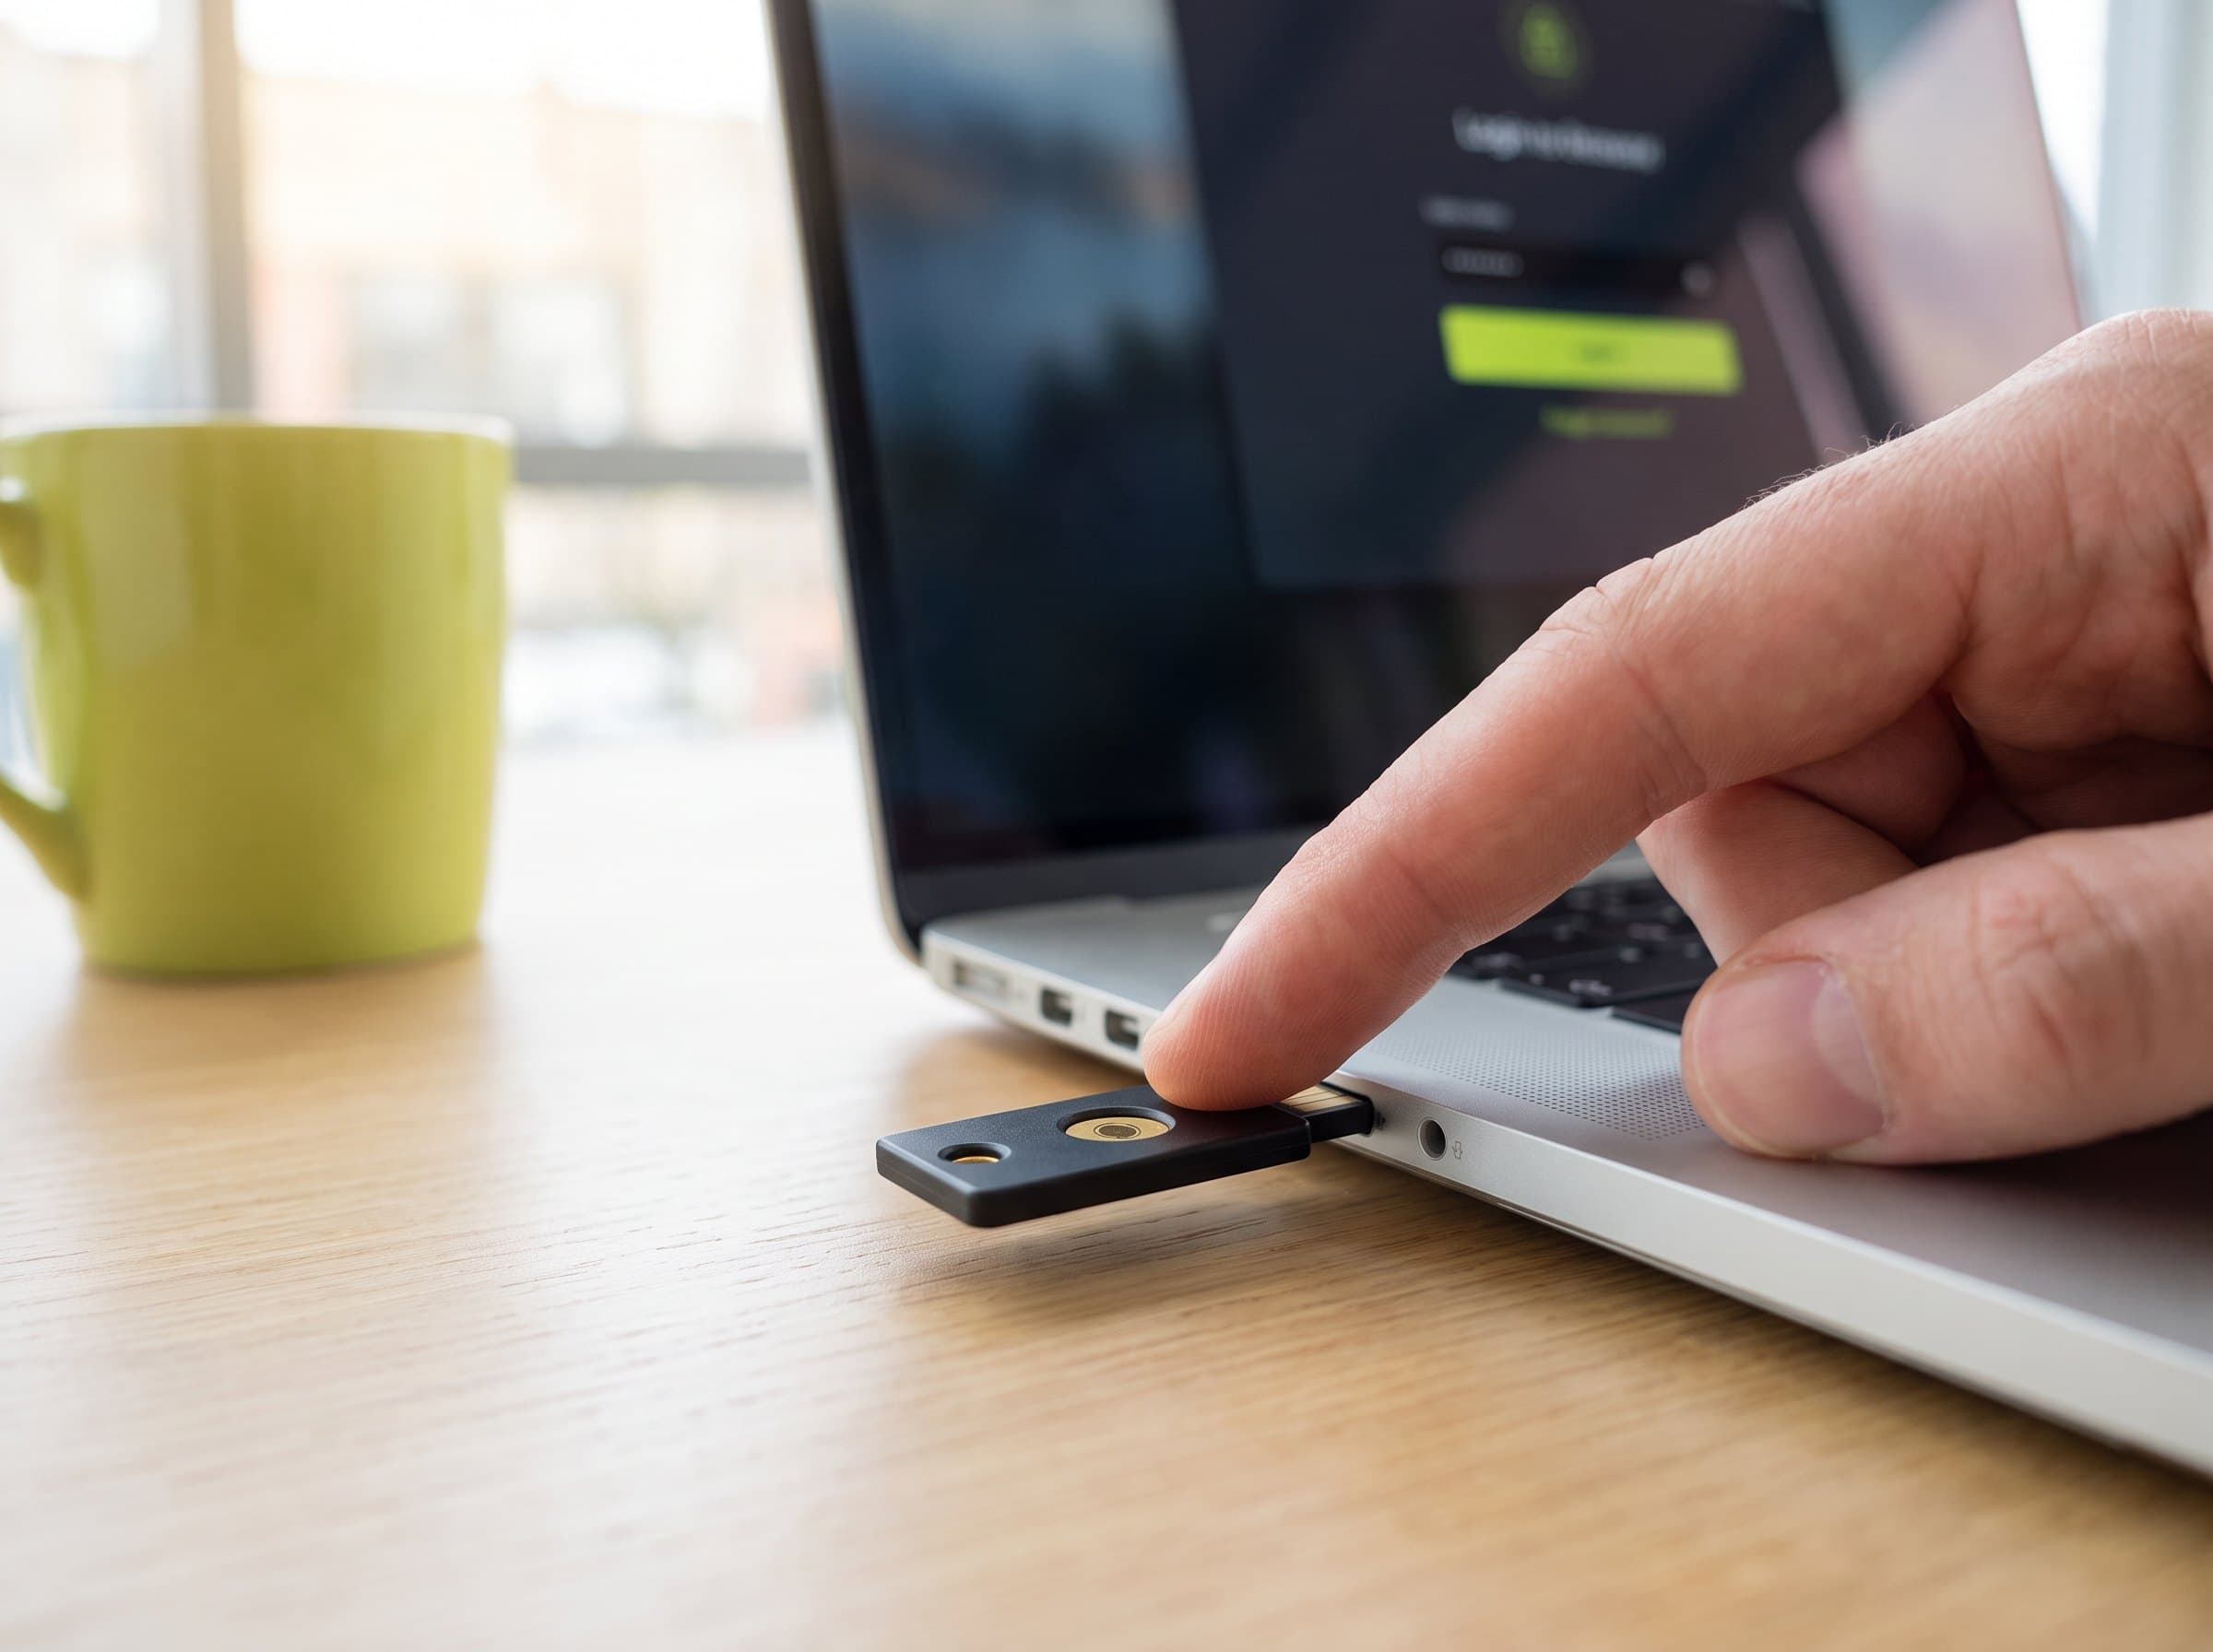
- Passwords should go — sign-in with a passkey or a security key such as YubiKey
- Auth0, Cognito & co. get expensive as the user count grows
- An existing Keycloak has grown over the years, is out of date — and nobody dares to update it
- The standard isn't enough: custom login steps or users from a legacy system
What we build
Keycloak can be extended through service provider interfaces (SPIs). We develop where the standard ends — as a separate, versioned module instead of a patch to the core, so updates stay possible.
Two-factor & passwordless
Passkeys and security keys such as YubiKey (WebAuthn) — as a second factor or for signing in with no password at all, plus TOTP apps. Phishing-resistant instead of one-time codes by SMS.
Login with ID Austria, Entra ID & ADFS
Identity brokering via OIDC or SAML: users sign in with an existing account, including from the on-premises Active Directory via ADFS. Keycloak handles the first login, linking to existing users and roles.
Federation of several Keycloaks
Several Keycloak instances, e.g. per organisation or tenant, connected via generic OIDC brokering — one login across organisational boundaries.
Custom extensions
Authenticators, event listeners, token mappers or a connection to an existing user database — as an SPI in Kotlin or Java, with tests.
Login in your own design
Login, registration and account pages as well as emails in your application's branding, multilingual.
Integration into your applications
OIDC clients for Spring Boot, React, Node and mobile apps, a well-designed role and group model, service accounts for machine-to-machine.
Operations on Exoscale
If the login fails, everything stops. That's why we run Keycloak on Exoscale SKS (Kubernetes) with the official Keycloak Operator and a managed PostgreSQL. If Keycloak should run in your own cloud or data centre, we set it up there, ideally on a Kubernetes cluster as well.
- Highly available with several instances
- Managed PostgreSQL with automatic backups
- Updates planned and tested on staging first — including custom extensions
- Custom extensions and theme in a versioned container image
- Monitoring and alerting for availability, login errors and certificates
- Login and admin events logged and available for audits
- Infrastructure as code, deployment via GitOps
Questions and answers
What does Keycloak cost?
Keycloak is open source (Apache 2.0 licence), there is no cost per user. You pay for development and operations — with many users usually cheaper than Auth0, Okta or Cognito, which charge per user.
We already have a Keycloak. Can you take it over?
Yes. We first review version, configuration and custom extensions, bring it up to date and then take over operations and updates.
Can Keycloak run in our own infrastructure?
Yes, in your cloud or on-premises. We recommend a Kubernetes cluster for it: with the official Keycloak Operator, several instances run with high availability and updates are rolled out in a controlled way through the operator. It works without Kubernetes too, but high availability and updates then take more manual work.
How much work do Keycloak updates take?
Keycloak releases frequently, and major versions regularly change configuration and APIs. With custom extensions as separate modules, tests and a staging environment, updates become routine instead of a risk.
What does connecting ID Austria take?
Technically, ID Austria is another identity provider that Keycloak connects via brokering. On top of that, your service has to be registered as a service provider — we take care of the technical side.
Our Active Directory runs on-premises. Does that work with Keycloak in the cloud?
Yes, via ADFS. Keycloak connects ADFS as an identity provider over SAML and the sign-in runs through the user's browser — Keycloak doesn't need a direct connection into your company network. If the AD is synchronised with Entra ID anyway, login via Entra ID is the simplest route. A direct LDAP connection is possible but needs a VPN from the cloud into the company network.
Do you offer SMS as a second factor?
Yes, as a custom extension through your SMS provider — but only as a fallback. SMS is vulnerable to SIM swapping and phishing. As the default we recommend passkeys, security keys or a TOTP app; SMS remains for users without an authenticator app or key.
Can we switch from Auth0, Cognito or a custom solution?
Yes. Users, roles and clients are migrated, passwords directly or on first login depending on the hash algorithm. Users don't have to set a new password.
Let's talk about your login
A new Keycloak, an extension or taking over an existing one: briefly describe your situation, and afterwards you'll know how we would approach it.
30 min · online · free